Sean Hartrich
Senior Site Reliability Engineer
Senior Site Reliability Engineer
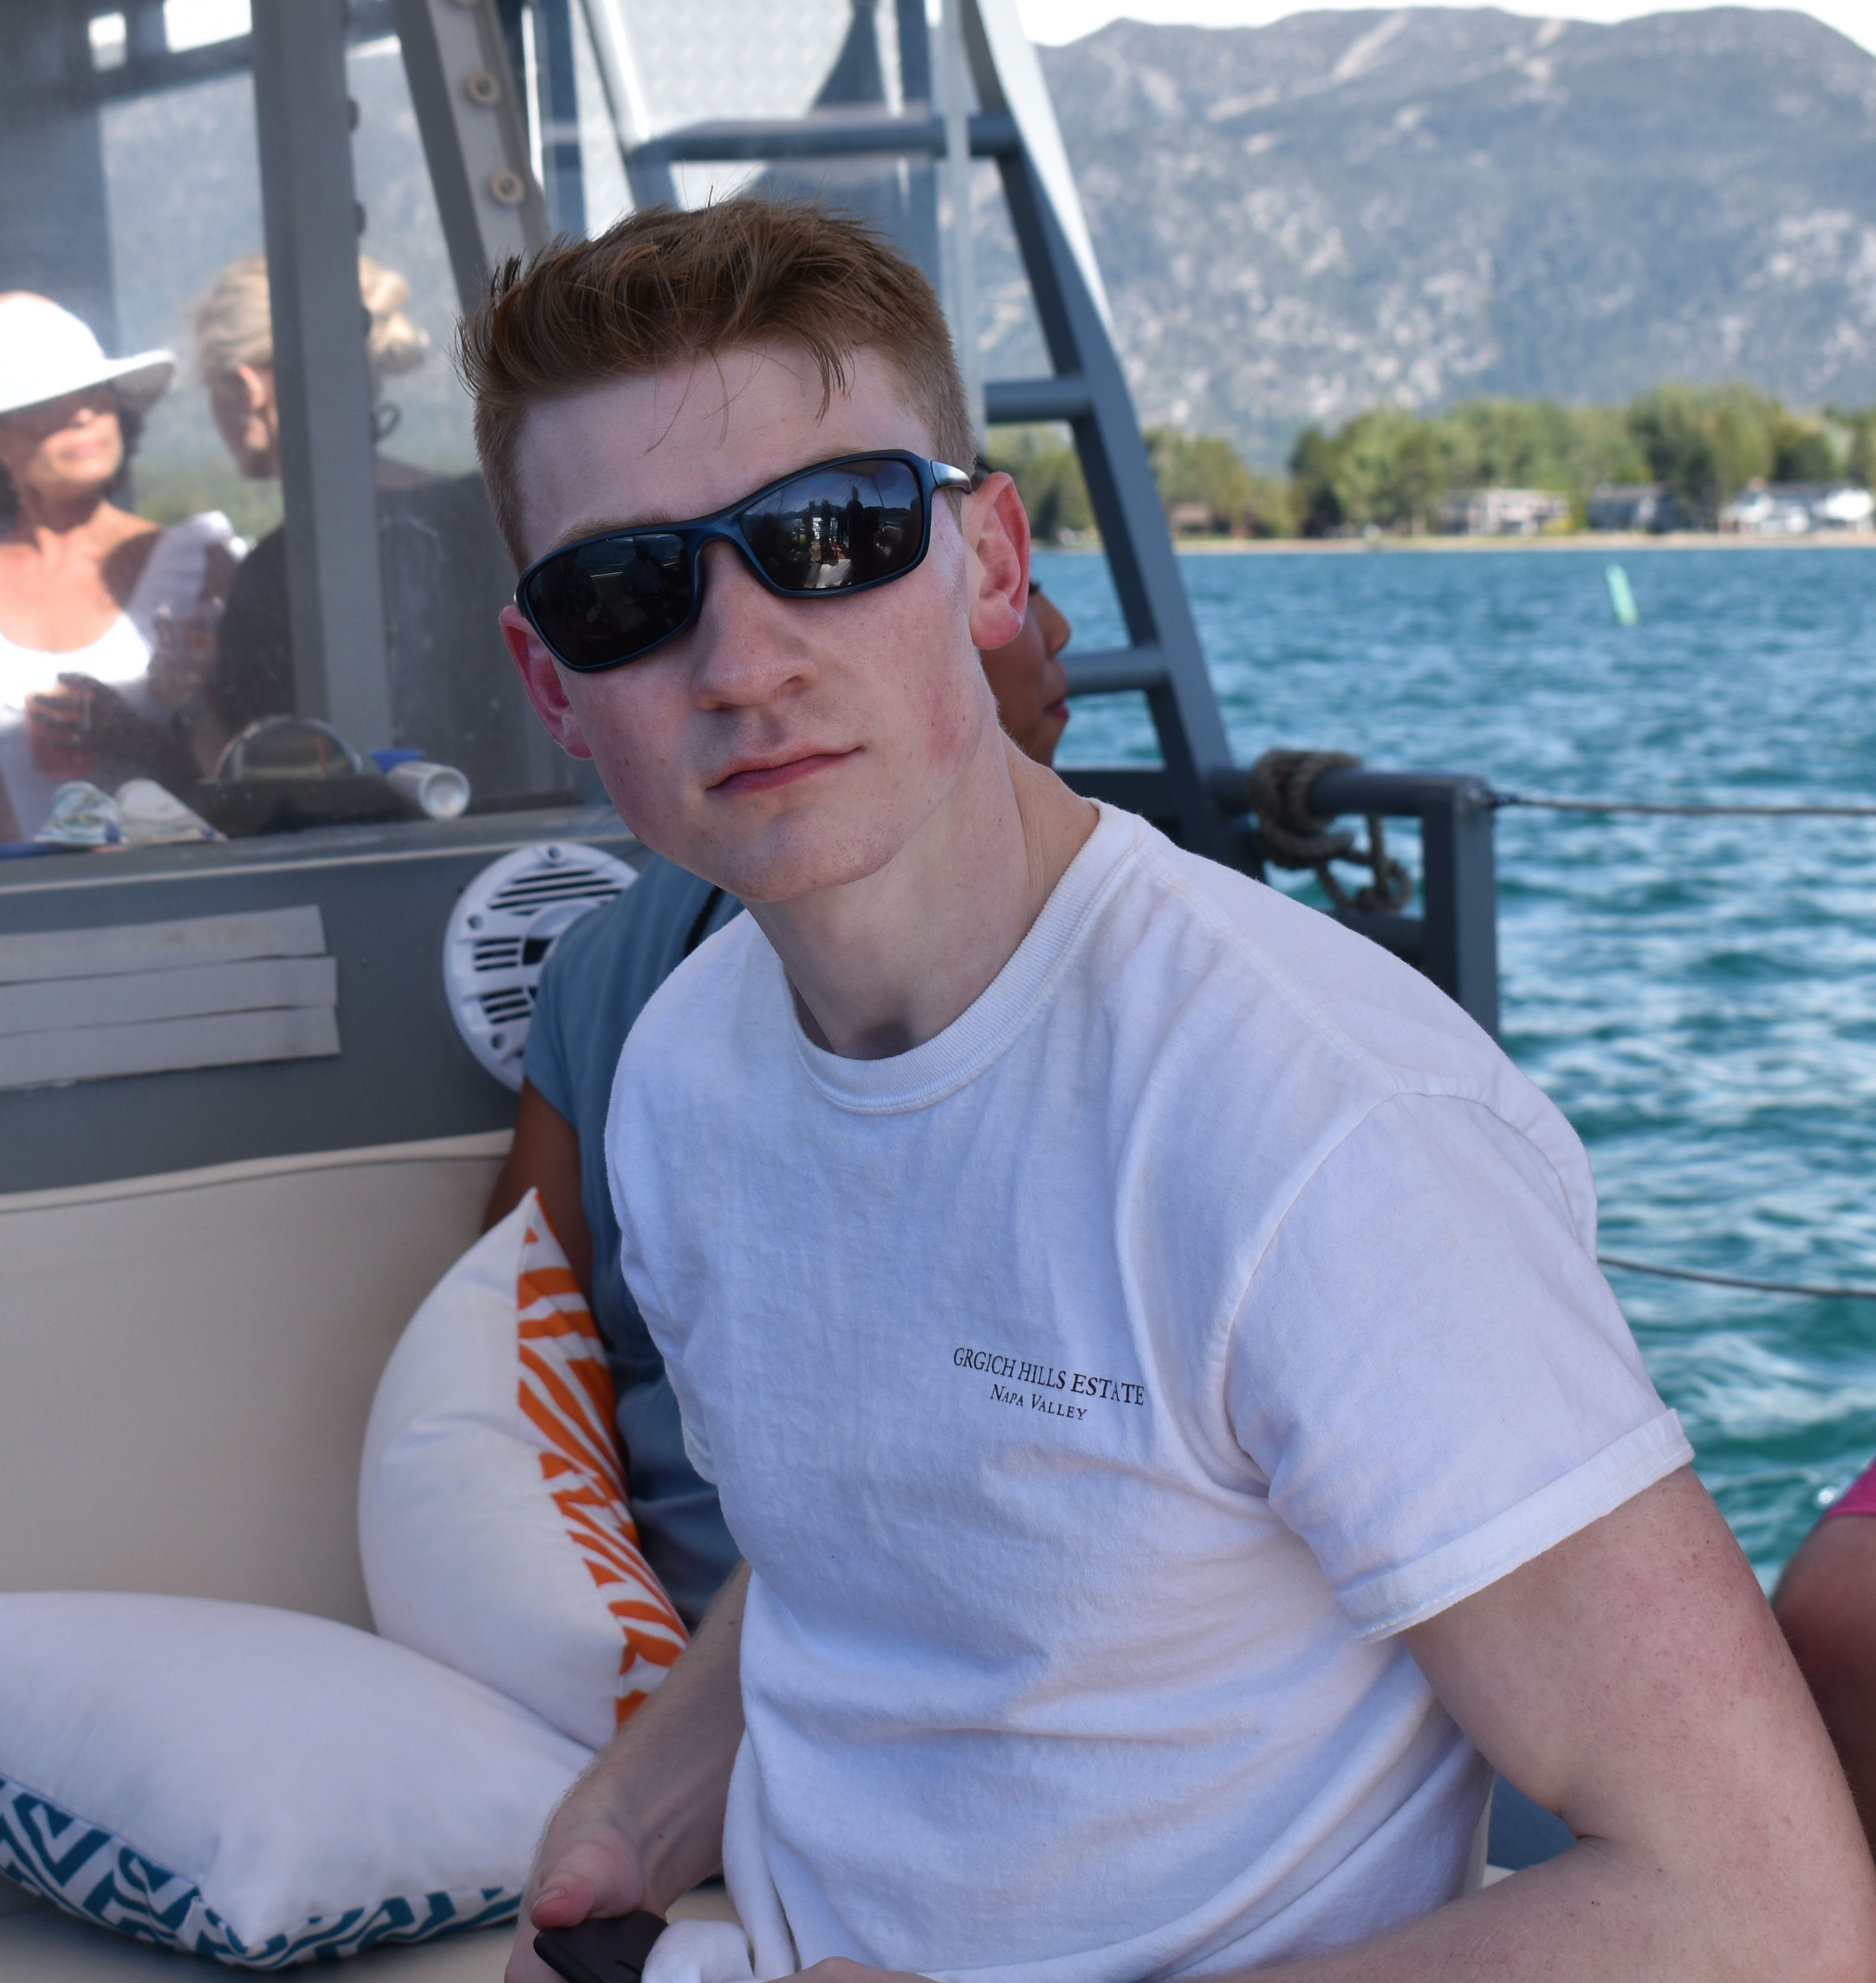
Sean is a Senior Site Reliability Engineer at Okta, where he architects, builds, and operates cloud infrastructure at enterprise scale. Specializing in AWS platform engineering, security automation, and federal compliance, he designs systems that serve every engineering team in Okta's Business Technology organization. From standing up production Kubernetes platforms on EKS to building automated security compliance pipelines across an entire AWS Organization, Sean approaches infrastructure as a full-stack discipline — owning systems from architecture decision through production operations and documentation. His work spans commercial and GovCloud environments, with deep expertise in identity, CI/CD, and security tooling.
Experience
Senior Site Reliability Engineer
July 2021 to Present
Okta | San Francisco, CA
As a Senior Site Reliability Engineer on Okta's Business Technology Reliability Engineering team, I architect, build, and operate production infrastructure serving the entire BT organization. I designed and built Okta BT's self-hosted JFrog Artifactory Enterprise Plus platform from scratch on EKS — covering architecture, Istio service mesh, CrowdStrike security hardening, Okta SSO/SCIM integration via the OPP agent, disaster recovery runbooks, and automated end-to-end testing. I architected an automated security compliance pipeline using AWS Config Rules, CloudFormation Stacksets, Lambda, EventBridge, and Cloud Custodian to detect and remediate misconfigurations across the entire BT AWS Organization. I maintain Okta's federal GovCloud infrastructure — including STIG-compliant GitLab upgrades, FIPS compliance deployments, VDI image pipeline automation, and monthly federal POAM inventory. I co-own the AWS account vending machine and serve as access provisioning gatekeeper for 40+ teams across the organization.
Software Engineer
May 2018 to July 2021
Zuora | Redwood Shores, CA
Architected and engineered enterprise data lake driving critical business insights (leveraging AWS Lambdas, Glue/Apache Spark, Athena, QuickSight, S3); designed Serverless AWS CloudFormation project template to rapidly generate pipelines for new data sources (structured and unstructured) in a matter of hours to ingest raw data, compress into parquet format, deduplicate records, and compile queryable Hadoop hive cluster. Engineered B2B Node-Express e-commerce platform selling/provisioning Zuora University and other training products, capturing millions of dollars annually. Developed Salesforce application to allow non-technical users to build customized workflows to execute cross-object aggregations in asynchronous scheduled batch jobs and real time events. Coordinated with Applications team for regular sprint planning, code-reviews, and other Agile practices.
Data Analytics Specialist
May 2017 to May 2018
Realogy | Deerfield, IL
Directed process automation for day-to-day reporting and transaction processing roles. Engineered Python report generating platform to automate and customize internal reporting. Redesigned internal performance tracking and delivered informative, interactive dashboards for multiple KPIs for all 27 US companies. Developed experience-based, quantitative productivity expectations for 200+ full-time employees (FTEs). Engineered staffing resource models for centralization to determine when to hire/train 128 new FTEs. Authored ad-hoc reports to senior leadership including COO and CFO.
Operations Data Analyst Intern
May 2016 to May 2017
U.S. Venture | Appleton, WI
Streamlined weekly and monthly site performance reports. Performed comprehensive analysis of power utilization resulting in significant tax savings (~$120k/year). Restructured site service protocol and data management for 54 North American locations with regression analysis model. Provided corrective actions for CNG equipment and used quantitative analysis to evaluate improvements. Modeled and optimized equipment lubricant and electrical consumption by forecasting demand.
Education
B.S. Industrial and Systems Engineering
August 2014 to May 2018
Georgia Institute of Technology | Atlanta, GA
Graduated with High Honors
Education
Georgia Institute of Technology
B.S. Industrial and Systems Engineering
August 2014 to May 2018
Graduated with High Honors
Skills
Cloud Infrastructure
Deep expertise across the AWS platform: EC2, EKS, IAM, S3, Lambda, RDS, EventBridge, SNS, CloudTrail, CloudWatch, Secrets Manager, ECR, DynamoDB, VPC/Networking. Comfortable operating at scale across both commercial and GovCloud (FedRAMP) environments.
Owns and maintains Okta's BT AWS Organization — including account vending pipeline, OU hierarchy, Service Control Policies (IMDSv2 enforcement, networking restrictions, credential rotation allowances), and access provisioning for 40+ teams.
Architected and built an end-to-end automated security compliance pipeline using AWS Config Rules, CloudFormation Stacksets, Lambda, EventBridge, and Cloud Custodian to detect and auto-remediate misconfigurations across an entire AWS Organization.
Owns Okta's Federal VDI image pipeline — migrated from GoLang/Packer/CodePipeline to Python/GitLab Runners; manages FIPS compliance encryption, workspace lifecycle automation, and PagerDuty alerting.
Operates Okta's federal GovCloud environment including STIG-compliant infrastructure, federal IAM hardening with IP restrictions and YubiKey MFA, and monthly POAM inventory obligations.
Platform Engineering & IaC
Primary IaC tool for all cloud infrastructure. Manages EKS clusters, AWS Organizations, account pipelines, networking, and service infrastructure across commercial and federal environments — over 1,400 commits across 32 repositories.
Deploys and operates production EKS clusters — including node group sizing, Bottlerocket AMIs, pod affinity/anti-affinity, IRSA (IAM Roles for Service Accounts), and JVM/Tomcat tuning for production JFrog Artifactory workloads.
Uses Helm charts and Kustomize overlays to manage Kubernetes workloads including CrowdStrike Falcon Operator, Istio service mesh, and JFrog Artifactory.
Lead engineer for Okta BT's self-hosted Artifactory Enterprise Plus instance — deployed on EKS with Okta SSO/SCIM via OPP agent, Istio and CrowdStrike hardening, disaster recovery runbook, and automated E2E artifact test suite.
Builds and maintains custom Docker images for CI/CD pipelines; integrates Chainguard hardened base images for GovCloud ECR; manages container security scanning with Twistlock/Qualys.
Security & Compliance
Deployed CrowdStrike Falcon node sensors across EKS clusters via Helm operator and Kustomize; drove cross-team engagement with Enterprise Security to extend Falcon coverage to BT SRE cloud infrastructure.
Uses Cloud Custodian with CloudTrail Lambda triggers for event-driven compliance remediation — auto-remediation of open security group rules, SSH port restrictions with edge case handling, and cross-account SNS notification routing.
Integrates Checkov static analysis into CI/CD pipelines to catch Infrastructure as Code security misconfigurations before they reach production.
Manages FIPS compliance deployments and STIG-compliant upgrade procedures for federal GitLab across multi-step major version upgrades; enforces immutable instance upgrade methodology for compliance posture.
Implements IMDSv2 enforcement org-wide via SCP, IP restriction policies for federal IAM users, breakglass IAM user management, and ABAC spike evaluations for dynamic SCP exception handling.
CI/CD & Developer Tooling
Builds GitHub Actions workflows with OIDC authentication, composite actions, and self-hosted runners (GHARC). Authored the BT-wide GitHub EMU migration guide enabling all engineers to migrate from GitLab CI to GitHub Actions.
Maintains GitLab CI/CD pipelines including the STIG-compliant federal GitLab instance, custom runner images, and cross-account role assumption for pipeline execution.
Maintains Okta's self-hosted GitHub Actions runner cluster — integrates Artifactory registry credentials, CrowdStrike sensor, E2E test workflows, and stress-tested alerting baselines.
Maintains Okta BT's Netbox IP address management platform; coordinates CIDR subnet allocation across new AWS account provisioning and networking architecture.
Uses Python for infrastructure automation (rewrote GoLang/Packer VDI pipelines in Python), Lambda functions, and compliance tooling. Uses Bash for CI/CD scripting and operational automation.
Identity & Observability
Works at the intersection of Okta product and infrastructure — configures SAML SSO, SCIM provisioning via Okta OPP agent with nginx SCIM proxy sidecar, and OIDC federation for EKS IRSA and GitHub Actions workflows.
Manages AWS IAM Identity Center for SSO/OIDC across the BT AWS Organization; maintains permission sets, account assignments, and OIDC provider configurations for Airflow EKS, Spinnaker, and GitHub.
Drives observability initiatives including ingesting Federal BT CloudTrail logs into BT Splunk; builds log transform Lambdas with custom sourcetype assignment for Kubernetes and managed-service VPCs.
Configures PagerDuty alerting for production infrastructure — WorkSpaces capacity limits, EKS cluster health, GitLab log volume, GHARC E2E test failures, and breakglass login events.
Designs CloudTrail-event-driven architectures for auto-tagging, alerting, and compliance; manages CloudWatch log groups, alarms, and dashboards across commercial and federal environments.
Projects
kns-audit
A command-line tool that audits Kubernetes namespaces for security and reliability issues — missing resource limits, absent health probes, insecure security contexts, and image hygiene problems. Exits non-zero on failures so it can act as a CI pipeline gate.
pi-observability
Self-hosted observability stack for home network monitoring built for Raspberry Pi. Three custom Python exporters feed Prometheus with network speed, DNS latency across resolvers (Google, Cloudflare, Quad9), and TLS certificate expiry — all visualized in auto-provisioned Grafana dashboards.
Network Speed Tracker
A Python script running on my home server that measures network speed throughout the day and persists results to S3. The live chart below pulls that data and renders download speed, upload speed, and ping latency over time using D3.js.
Home Air Quality Monitor
A Raspberry Pi logs indoor particulate matter readings — PM2.5 and PM10 — and persists them to S3 as they are collected. The live chart below pulls that data and plots both figures over time with D3.js.
News Analysis
Aggregates news headlines on a rolling 7-day basis and performs K-means cluster analysis to surface topic groupings across current events. Cluster results are rendered as an interactive scatter plot using Python's Bokeh visualization library.
Network Speed Tracker — Live Data
Live network speed readings from my home network, taken every 30 minutes. Ping is plotted against the right-hand axis.
PM2.5 — Fine Particulate Matter
Particles under 2.5 micrometres, the fraction most associated with health effects. Background shading and dashed lines mark US EPA AQI categories — those are defined on 24-hour averages, so a brief crossing here is a rough guide rather than an official AQI reading.
PM10 — Coarse Particulate Matter
Particles under 10 micrometres. PM10 boundaries sit far higher than PM2.5, which is why the two are charted separately rather than sharing an axis.